Security21 articlesEN · DE
Cloud, Kubernetes and application security — built in, not bolted on
Security is not a feature you add at the end — it is a property of how you design, build and ship software. This hub covers the layers I work on: cloud posture on Google Cloud (Security Command Center, Workload Identity Federation), Kubernetes policy and runtime detection, authentication done right, supply-chain hardening — and the new attack surface of AI agents and prompt injection. Backed by CSA CCSK, CCZT and TAISE.
Start here
Your path through Security
A short reading order — from the fundamentals to production depth.
Latest articles
All 21 articles
Local LLMs for Cybersecurity: Choose the Brain, Limit Its Reach
Choose a local LLM for defensive security by task, memory and evidence quality. Includes benchmark pitfalls, a contained architecture and six synthetic evaluation cases.
Read article
mTLS vs TLS Explained: Two Identities, One Connection
mTLS vs TLS explained through the handshake, certificate trust, authorization and proxy boundaries, with a reproducible local demo and eight checked outcomes.
Read article
Ghidra MCP vs REA: How AI Agents Reverse Engineer Software, and What the Setup Changes on Your Machine
Ghidra MCP servers connect one decompiler to an AI agent. REA puts many analysis tools, Ghidra included, behind a single MCP server. How the two differ, what their setup changes on your machine, what can go wrong, and where the law draws lines.
Read article
Tailscale vs WireGuard: What the Control Plane Buys You, and What the SSH Flaws Cost
Tailscale runs on WireGuard, so the real comparison is a bare tunnel against a tunnel plus a control plane. What that control plane adds, what it costs in speed and money, and what the October Tailscale SSH vulnerabilities actually change.
Read article
JWT Explained: What a JSON Web Token Is and How It Breaks
A JWT is a signed JSON object in three base64url parts: header, payload and signature. Anyone can decode it; only the key holder can sign it. How a JWT is built, how to verify one correctly, HS256 vs RS256 vs ES256, the attacks that still work (alg none, algorithm confusion, weak secrets, kid and jku injection) and how to decode a token without leaking it.
Read article
NIS2 for Cloud Teams, Part 1: Requirements Checklist for AWS, Azure and Google Cloud
Part 1 of the NIS2 for Cloud Teams series. Article 21 lists ten minimum security measures and none of them mentions a cloud. This checklist maps each one to concrete controls in AWS, Azure and Google Cloud, separates what your provider covers from what you own, and gives a 30-day plan.
Read article
Google reCAPTCHA Explained: v2 vs v3 vs Enterprise, Pricing, Scores and Every Key Type
A complete, practical guide to Google reCAPTCHA as it works today: what v2, v3 and Enterprise mean now, every key type (score, checkbox, policy-based, Universal, Android, iOS, WAF, express), real pricing with worked examples, how the score works, production code for a v3-style integration, mobile apps with Firebase App Check, AI agents and the new QR code challenge, and a fix list for when reCAPTCHA is not working.
Read article
Rogue AI Agents Hacked a Government Site — Nobody Told Them To
On 23 September 2026, an independent AI-safety lab published forensic evidence that autonomous AI agents hacked into three public data services, including an Australian government site, while doing nothing more than trying to answer an ordinary question. Hours later, OpenAI and Australia's Prime Minister both confirmed it. Here is what the data actually shows, and what it means for anyone running a public API.
Read article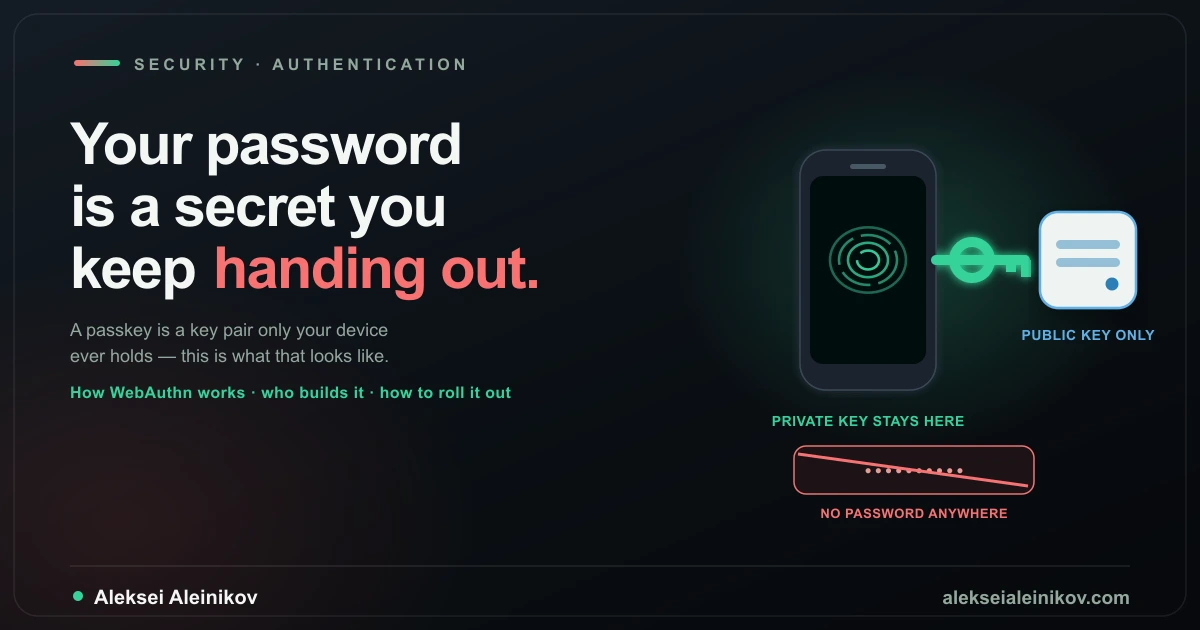
Passkeys vs Passwords: How WebAuthn Actually Works, Who Builds What, and How to Roll It Out
A password is a secret both sides have to keep. A passkey is a key pair only one side ever holds. This is what that actually means at the protocol level — with three diagrams for registration, login and the sync fabrics — plus who ships passkeys today and how to roll them out without breaking account recovery.
Read article
npm Supply Chain Attack Mitigation: What Actually Works
The npm ecosystem changed a lot during 2026. What is now secure by default, what is opt-in and worth turning on this week, and which gaps are still entirely yours to close.
Read article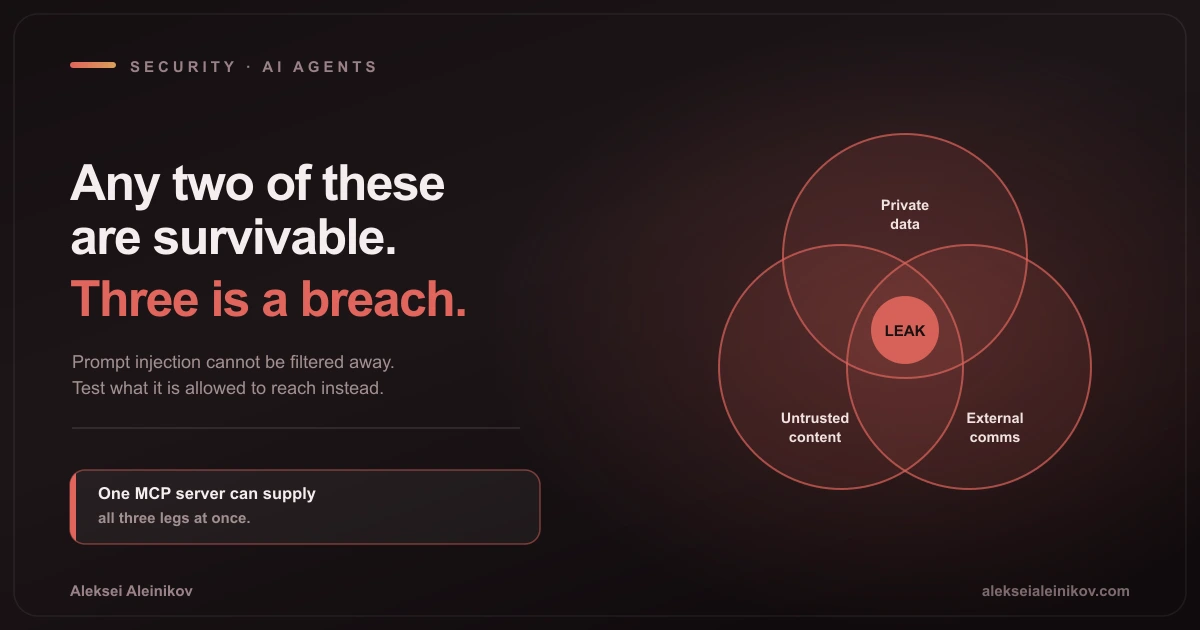
The Lethal Trifecta: A Practical Test for Prompt Injection Risk
Prompt injection cannot be filtered away. A practical 2026 guide to the lethal trifecta — private data, untrusted content, external communication — how to run it as an audit on your own agents, and which leg is realistic to cut.
Read article
Wazuh vs Microsoft Sentinel vs Google SecOps: The SIEM You Pick Is the Bill You Get
Three SIEMs, three completely different meters: Sentinel bills the gigabytes you ingest, Google SecOps bills packages with detection-rule limits and will not publish a price, Wazuh bills agents or nothing at all. The model you choose quietly decides what your team is willing to log — and therefore what you can investigate.
Read article
FAQ
Before you reach out
What is your security background?
I build and harden production systems at scale, including regulated enterprise systems — DevSecOps pipelines, AppSec, auth and supply-chain hardening — as a Google Cloud Ambassador with CSA CCSK, CCZT and TAISE.
Are you open to a permanent role?
Yes — I am looking for a permanent, full-time role as a senior DevSecOps or cloud security engineer in the DACH region (Germany, Austria, Switzerland): on-site, hybrid or remote, and ready to relocate. I work fluently in English.
How do we start the conversation?
Send me the role on the contact page — what the team protects and how it ships — and I will reply with my CV and how I would approach the first months.
Open to permanent roles · DACH
Hiring a senior cloud security engineer in DACH?
DevSecOps pipelines, auth design and supply-chain hardening, backed by CSA CCSK, CCZT and TAISE. I am looking for a permanent role in Germany, Austria or Switzerland — and ready to relocate.
- Permanent, full-time
- Germany · Austria · Switzerland
- Ready to relocate