 Featured
Security
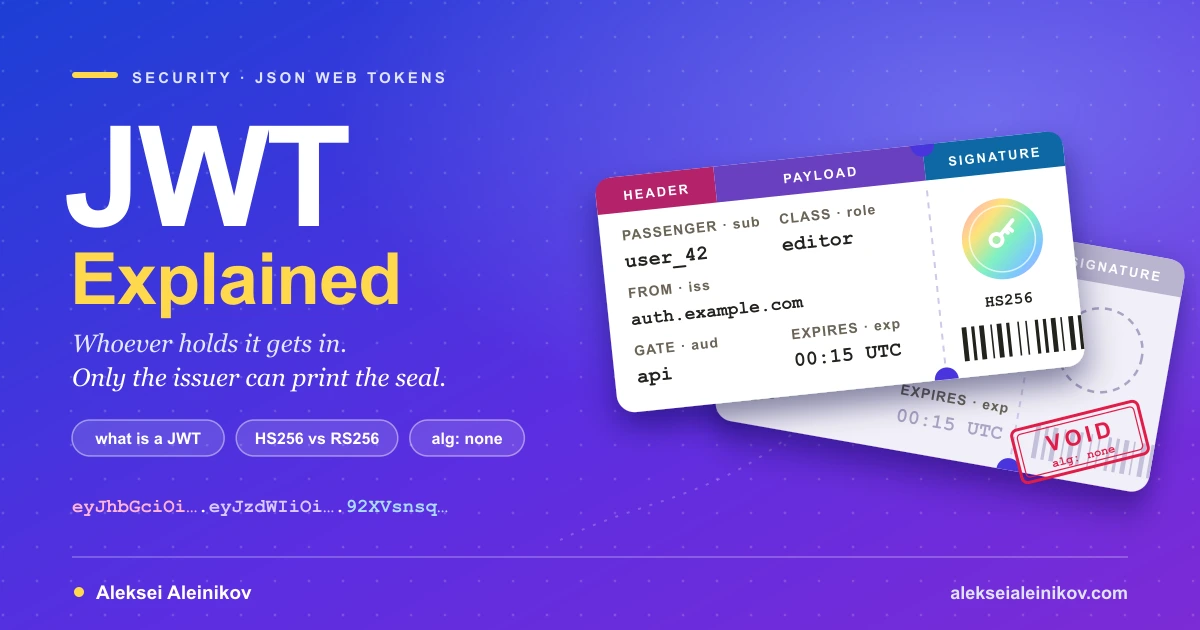
JWT Explained: What a JSON Web Token Is and How It Breaks
A JWT is a signed JSON object in three base64url parts: header, payload and signature. Anyone can decode it; only the key holder can sign it. How a JWT is built, how to verify one correctly, HS256 vs RS256 vs ES256, the attacks that still work (alg none, algorithm confusion, weak secrets, kid and jku injection) and how to decode a token without leaking it.
Key takeawayA JWT is three base64url parts joined by dots: a header, a JSON payload of claims and a signature over both. Base64url is an encoding, not encryption, so anyone holding the token can read every claim.